Findings and Improvements
Description of the identified vulnerabilities and the progress made during the assessment, with recommendations to maintain and consolidate the enhanced defenses.


Purple Team Assessment (PTA)
Specialist services to protect your business
The PTA (Purple Team Assessment) service by ISGroup is designed to enhance the detection and response capabilities to cyber attacks through an interactive approach that integrates testing activities and continuous improvement.
This process does not stop at merely identifying vulnerabilities but aims to strengthen corporate defenses in real-time, preparing security personnel to respond to realistic attack scenarios.
The Purple Team Assessment combines the expertise of the Red Team and the Blue Team, offering a customized evaluation that adapts to the specific needs of the client's infrastructure.
The goal is to enhance the organization's ability to detect, respond to, and mitigate attacks effectively, improving both security technologies and operational processes.
The Purple Team Assessment by ISGroup differs from the traditional Red Team Assessment as it does not limit itself to simulating attacks in a "black-box" context.
Instead, it leverages active interaction with the defensive team to refine detection and response capabilities to ongoing attacks. This approach allows for testing specific security aspects and improving defenses iteratively.
The steps of the Purple Team Assessment are similar to those of a Red Team Assessment, but the goal is different: to create a continuous improvement cycle based on immediate feedback between the teams involved, to strengthen the corporate security infrastructure.
The report describes the vulnerabilities identified in the infrastructure and assesses the measures used to prevent, detect and mitigate attacks.
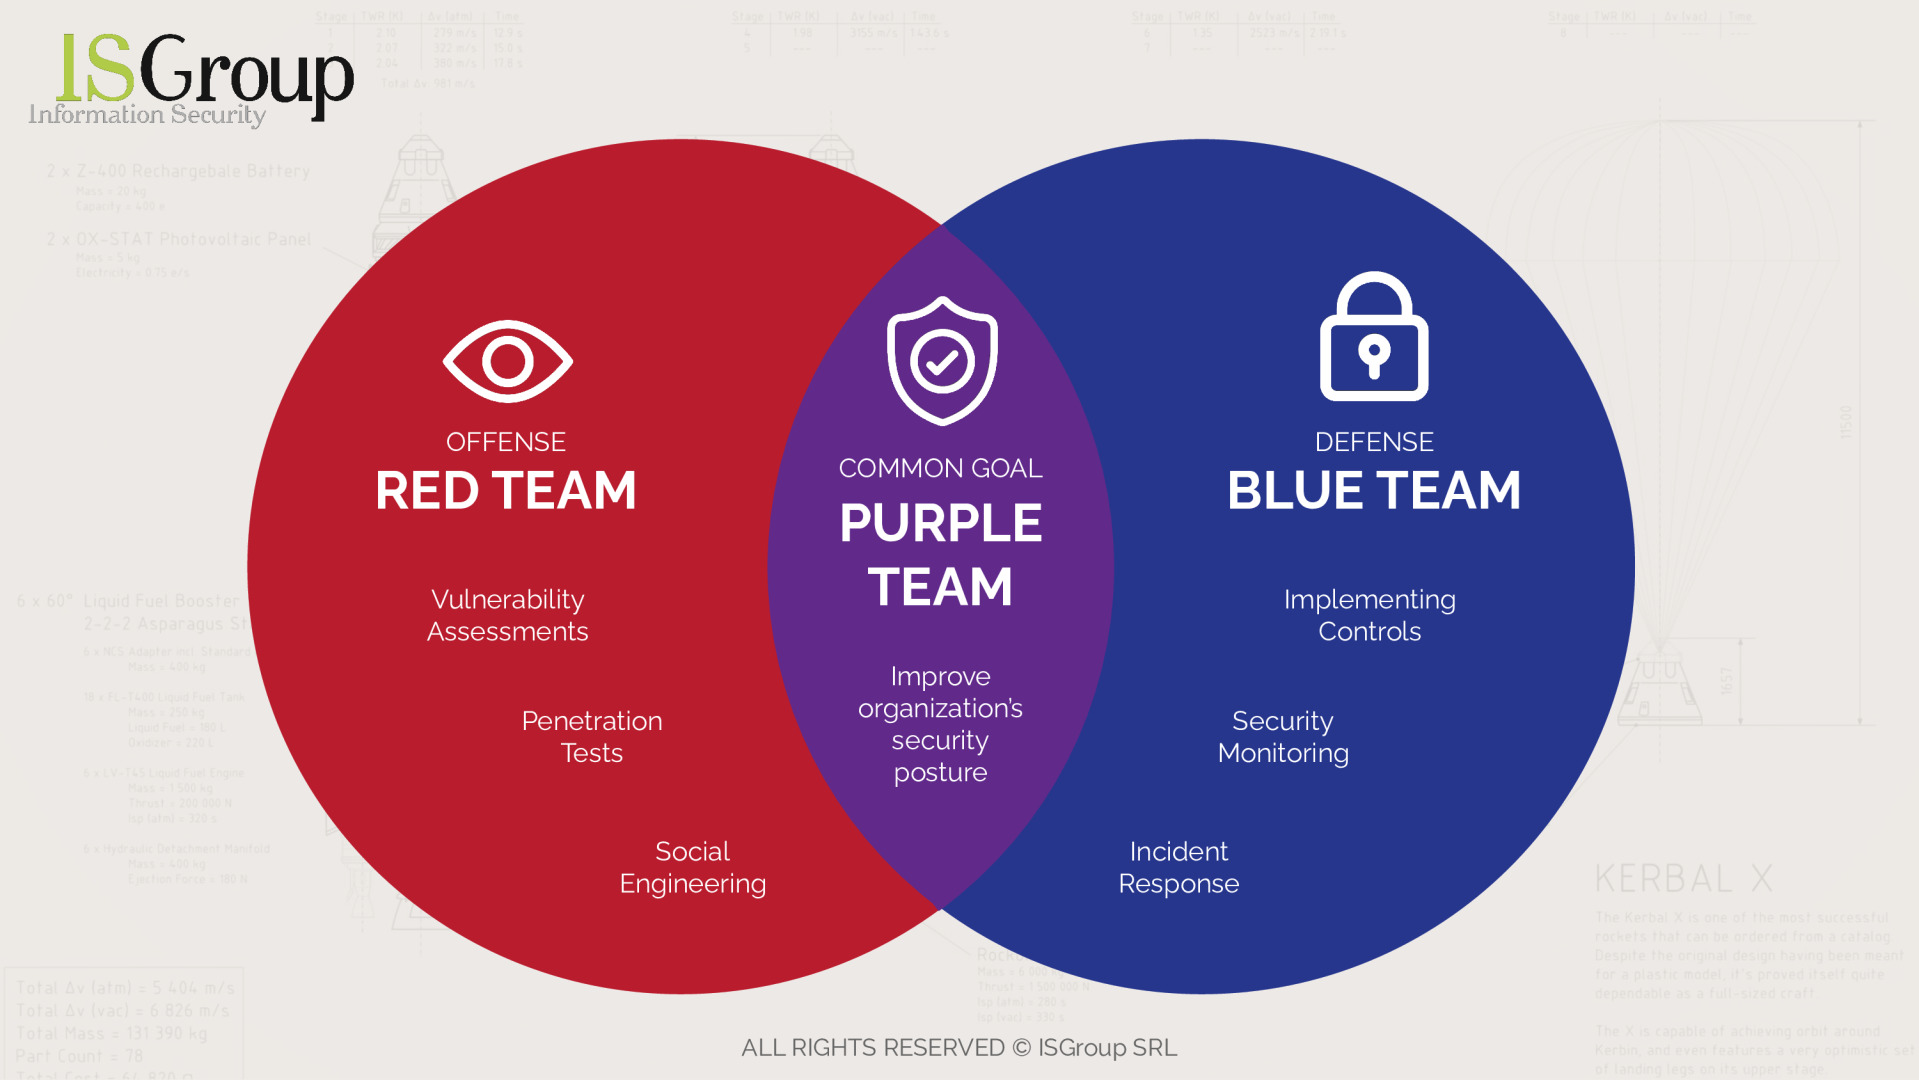
The Purple Team Assessment by ISGroup is structured in the following phases:
Data Collection Phase
The first phase involves an in-depth study of the corporate infrastructure to understand the current capabilities of detecting and blocking attacks.
Risk Assessment
Using industry-standard frameworks, such as MITRE ATT&CK and NIST, the risk analysis is customized to fit the client's specific needs, identifying and managing the most relevant risk factors.
Execution
During this phase, ISGroup's defensive team and the company's internal team work together to detect and block simulated attack attempts. If attacks are detected, ISGroup guides the team through the response process; otherwise, detection, alert, and logging systems are enhanced.
Risk Evaluation
At the end of the execution, risks are evaluated based on the outcomes of the simulated attacks, providing specific recommendations to further strengthen defenses or improve identified areas of weakness.
You will receive a report on the assessment process, divided into three sections.
Description of the identified vulnerabilities and the progress made during the assessment, with recommendations to maintain and consolidate the enhanced defenses.
An analysis of the defensive team's detection and response capabilities, with evaluations of the techniques used, reaction times, and the effectiveness of the countermeasures adopted. A specific improvement plan is provided to optimize these capabilities.
A technical and strategic guide for IT security managers, with instructions on how to implement the suggested changes and how to maintain a continuous improvement cycle of defenses. This section includes strategies to refine defenses and improve the overall security posture of the organization.
The Purple Team Assessment combines offensive and defensive activities to improve the organisation's ability to detect and respond to simulated attacks. The Red Team, defensive team and internal staff collaborate in a verification and improvement cycle. For a broader offensive attack path, Ethical Hacking is available.
The Purple Team Assessment involves active interaction with the defensive team and feedback during the activity, whereas a Red Team Assessment can use a more separate, black-box approach. The choice depends on the assessment objective.
The Purple Team Assessment includes infrastructure data collection, risk assessment, execution of simulated attacks with the defensive team, and final evaluation. The scope adapts these phases to the customer's needs.
The Purple Team Assessment report describes findings and improvements, analyses detection and response capabilities, and proposes a continuous improvement strategy.
The cost of a Purple Team Assessment depends on the infrastructure, the number and complexity of attack scenarios, and the work carried out with the defensive team. The proposal states the assessment effort and includes reporting on findings, detection, response, and improvements.
Shape your security priorities into a tailored proposal