Executive Summary
Provides management with a non-technical summary of Anti-DDoS activities and relevant events.


Defend service availability
DDoS mitigation for servers, web applications and connectivity
DDoS attacks are among the most common and damaging for a company. These attacks aim to make a specific service unusable.
DDoS attacks usually:
Overload the bandwidth by sending numerous requests to a server;
Abuse the machine by using all its resources, rendering it unable to handle traffic;
A DDoS attack can make websites, applications and connectivity unavailable, interrupting services used by customers and staff.
Anti-DDoS detects and mitigates DDoS traffic to keep protected services available and reduce the impact of the attack.
The Anti-DDoS service protects web applications, servers and connectivity through measures configured at the perimeter and on exposed services.
ISGroup manages configuration, monitoring and adaptation of protection over time according to the technologies and architecture in place.
Countermeasures are defined for the volumetric, protocol and application attacks included in scope, to filter malicious traffic and limit the impact on legitimate services.
Mitigates DDoS traffic directed at exposed applications
Applies and maintains mitigation measures on protected servers
Reduces the impact of malicious traffic on connectivity
The Anti-DDoS service follows agreed activities for analysis, configuration, monitoring and adaptation of protection.
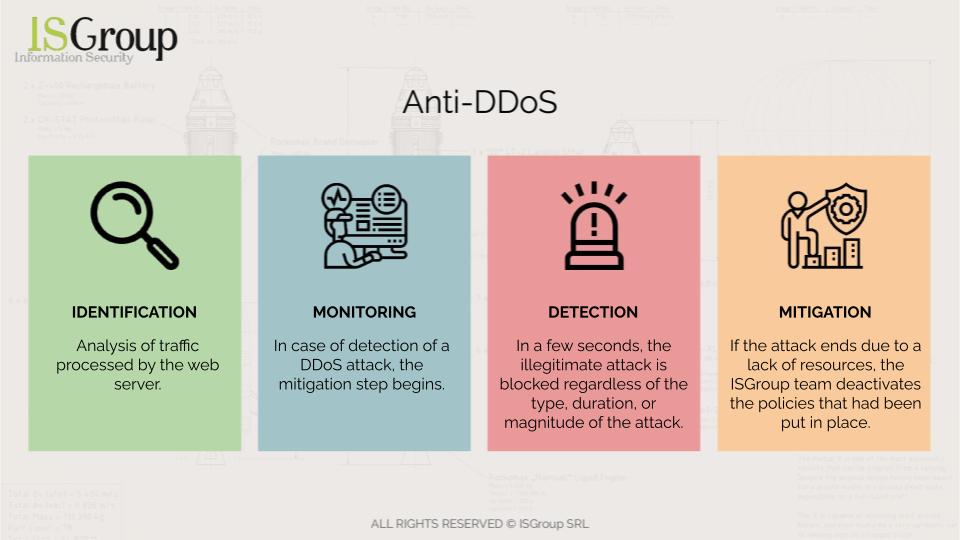
ISGroup manages the activities included in the service scope and supports the analysis of events related to DDoS attacks.
Summarizes configuration, applied protection and events observed within the service scope.
Provides management with a non-technical summary of Anti-DDoS activities and relevant events.
Documents the protected scope and the main countermeasures configured.
Reports observed events and operational guidance emerging from monitoring.
ISGroup Anti-DDoS protects web applications, servers, and corporate connectivity. Assets, flows, and protection boundaries are defined in the agreed scope.
The Anti-DDoS service includes configuration, management, monitoring, and adaptation of protection over time for assets within the agreed scope. Operating methods, responsibilities, and escalation are specified in the proposal.
The solution is designed without requiring a specific pre-existing technology. Actual compatibility nevertheless depends on the architecture, connectivity, applications, and configurations involved. ISGroup checks these elements before defining the work.
No. Protection aims to reduce exposure to and impact from DDoS attacks but does not guarantee absolute availability or absence of downtime. Results and limits depend on the scope, architecture, and attack characteristics. Any service levels must be stated in the contract.
Anti-DDoS protection is an ongoing service: after the initial configuration, it includes management, monitoring and adaptation of protection over time for web applications, servers and corporate connectivity.
Shape your security priorities into a tailored proposal